Why 30% of Merchants Fail PCI DSS Level 1 Certification
WRITTEN BY
Dylan Coombs
Citcon
Commercial Leader
Date
Oct 4, 2026
Subscribe to our interesting updates
SHARE ON
PCI DSS Level 1 certification is essential for merchants processing over 6 million card transactions annually. In 2025, 30% of merchants failed to achieve this certification, impacting their ability to manage sensitive payment data securely.
What is PCI DSS: PCI DSS (Payment Card Industry Data Security Standard) is a set of security standards designed to ensure that all companies that accept, process, store, or transmit credit card information maintain a secure environment.
The global e-commerce market is expected to reach $6.4 trillion by 2025, with payment card transactions being a significant part of this growth. However, the rise in cyber threats has led to increasing scrutiny on how companies protect sensitive customer data. In this context, PCI DSS compliance is not merely a regulatory requirement but a critical business strategy. Achieving PCI DSS Level 1 certification can significantly mitigate risks associated with data breaches, which, according to the IBM Cost of a Data Breach Report 2025, averaged $4.45 million per incident.
Context
PCI DSS Level 1 certification is vital for large merchants. It indicates that a business adheres to the highest security standards in the payment industry.
Merchants can face severe penalties for non-compliance, including hefty fines and reputational damage. A 2026 study by the PCI Security Standards Council revealed that 40% of merchants who failed to comply with PCI DSS faced increased transaction costs due to chargebacks and fraud.
- Enhances Customer Trust: Achieving Level 1 certification assures customers that their payment information is secure.
- Reduces Fraud Risk: Compliance significantly lowers the chances of data breaches and fraud.
- Improves Operational Efficiency: Streamlined processes and better security protocols enhance overall business operations.
- Regulatory Compliance: Staying compliant with PCI DSS helps avoid legal penalties.
Core Challenge
Many merchants struggle with the rigorous requirements of PCI DSS Level 1 certification. This certification requires a comprehensive security assessment and validation by a qualified security assessor.
The costs associated with achieving and maintaining this level of compliance can be daunting. According to a recent report, the average cost for Level 1 certification can range from $50,000 to $250,000, depending on the complexity of the business's payment systems.
Failure to achieve certification not only results in financial penalties but can also lead to increased exposure to cyber threats, which can result in significant financial losses. Businesses that do not comply may face fines from card brands, which can be up to $100,000 per month.
- Financial Penalties: Non-compliance can lead to fines from payment processors and card brands.
- Reputational Damage: Data breaches can severely impact customer trust and brand reputation.
- Increased Liability: Merchants may become liable for fraud and chargebacks.
- Operational Disruptions: Non-compliance can lead to disruptions in payment processing.
How to Achieve PCI DSS Level 1 Certification
Achieving PCI DSS Level 1 certification involves several key steps, including a thorough assessment of existing security measures and implementing necessary changes.
The first step is to conduct a gap analysis to identify areas needing improvement. Following this, businesses should enhance their security infrastructure, which may include firewalls, encryption, and access controls.
Finally, a qualified security assessor must perform a detailed assessment to validate compliance with the standards.
- Conduct a Gap Analysis: Identify areas where current practices fall short of PCI DSS requirements.
- Enhance Security Measures: Implement the necessary security controls to protect cardholder data.
- Engage a Qualified Security Assessor: Hire a professional to validate compliance and conduct the assessment.
- Complete and Submit the Self-Assessment Questionnaire: Depending on the business size, complete the appropriate SAQ.
Deep Dive into PCI DSS Requirements
PCI DSS consists of various requirements categorized into six key objectives aimed at protecting cardholder data.
The six objectives include building and maintaining a secure network, protecting cardholder data, maintaining a vulnerability management program, implementing strong access control measures, monitoring and testing networks, and maintaining an information security policy.
Each of these objectives includes specific requirements that organizations must meet to achieve compliance.
- Build and Maintain a Secure Network: This includes installing and maintaining a firewall configuration and changing default passwords.
- Protect Cardholder Data: Encrypt transmission of cardholder data across open and public networks.
- Maintain a Vulnerability Management Program: Use and regularly update anti-virus software.
- Implement Strong Access Control Measures: Restrict access to cardholder data on a need-to-know basis.
ROI and Business Case for PCI DSS Compliance
Investing in PCI DSS Level 1 certification can yield significant returns for merchants. Not only does it protect against data breaches, but it also enhances customer trust and loyalty.
According to a 2026 study, businesses that achieved PCI DSS Level 1 certification saw a 25% increase in customer retention and a 15% boost in sales due to improved customer trust.
- Increased Revenue: Enhanced customer trust can lead to increased sales.
- Cost Savings: Reducing the risk of data breaches can save businesses from hefty fines and legal costs.
- Operational Efficiency: Streamlined compliance processes lead to better resource allocation.
- Competitive Advantage: Certification can differentiate businesses in a crowded market.
How Citcon Solves This Challenge
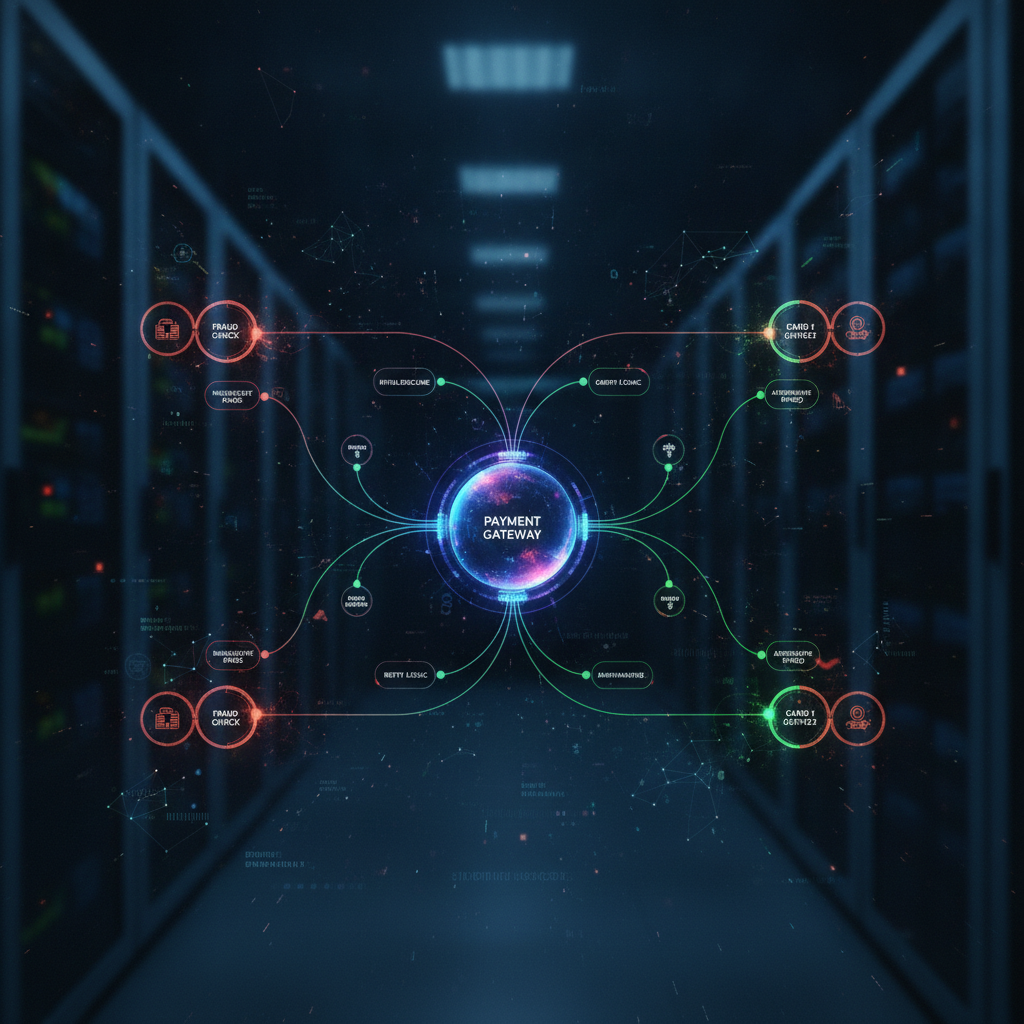
Citcon offers a streamlined solution for achieving PCI DSS Level 1 certification through its single API, which integrates over 100 payment methods. This simplifies compliance and reduces the burden on merchants.
Additionally, Citcon’s platform supports Buy Now Pay Later (BNPL) options, further enhancing the customer experience while maintaining strict compliance with PCI DSS Level 1 standards.
For further insights into payment strategies, check out our posts on payment opportunities with international guests and bank transfers vs digital wallets for tuition payments.
What are the benefits of PCI DSS Level 1 certification?
The benefits of PCI DSS Level 1 certification include enhanced customer trust, reduced fraud risk, and improved operational efficiency.
How long does it take to get PCI DSS Level 1 certified?
The duration to achieve PCI DSS Level 1 certification can vary, but it typically takes several months, depending on the complexity of the organization's systems.
What happens if a merchant fails PCI DSS Level 1 certification?
If a merchant fails PCI DSS Level 1 certification, they may face significant fines, increased transaction fees, and reputational damage.
Is PCI DSS Level 1 certification mandatory?
PCI DSS Level 1 certification is mandatory for any merchant processing over 6 million credit card transactions annually.
What are the costs associated with PCI DSS Level 1 certification?
The costs for achieving PCI DSS Level 1 certification can range from $50,000 to $250,000, depending on the business size and complexity.
Can small businesses achieve PCI DSS Level 1 certification?
While small businesses can achieve PCI DSS Level 1 certification, it is typically more relevant for larger merchants processing millions of transactions.
Key Takeaways
- PCI DSS Level 1 certification is essential for large merchants.
- 30% of merchants failed to achieve this certification in 2025.
- Investing in compliance can yield a 25% increase in customer retention.
- Non-compliance can lead to fines of up to $100,000 per month.